The North Korean Hacker Crime Story Inside a US Company
· based on the channel Max Crime
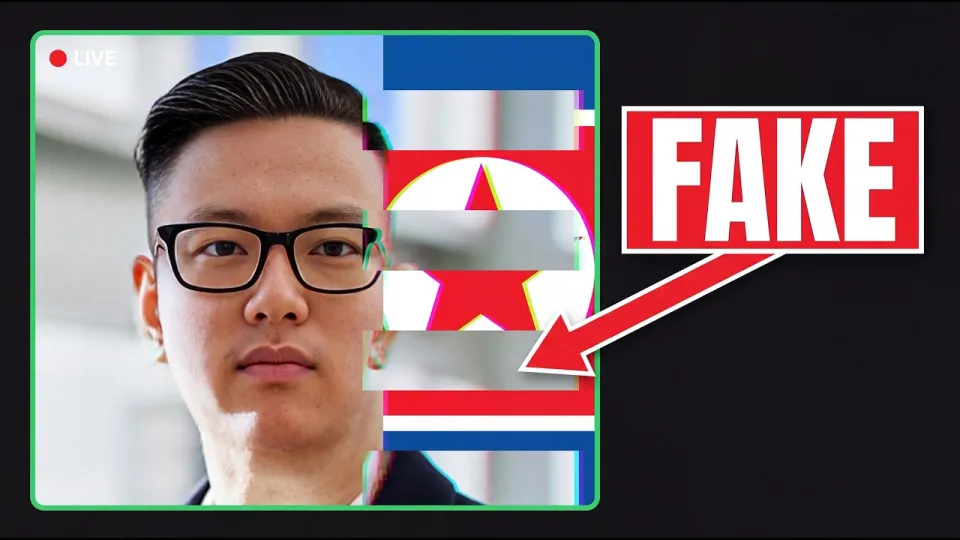
The crime story begins with a paradox: a cybersecurity company whose entire business is teaching employees to recognize fakes hired a North Korean IT worker anyway. The new hire cleared four video interviews, a background check and an identity review, then triggered malware alerts the moment his company laptop was switched on. His name belonged to a real American, his photo had been altered with AI, and the salary was being routed to the North Korean regime.
How a North Korean IT worker gets hired by a US company
The fraud is an employment scam, not a network intrusion: the worker applies for a legitimate remote job, passes the hiring process, and then turns the access he is given into money and intelligence. The mechanics repeat across cases.
- Identity theft. Operators buy or steal the credentials of a real US citizen — Social Security number, address, passport scan — often from data breaches or people willing to sell their identity for a cut.
- An AI-altered face. Application photos are edited so the face matches nothing in public records, while still passing automated checks. The photo KnowBe4 later published came from exactly this kind of submission.
- Interviews by video. The candidate appears live on camera, sometimes with a stand-in or a filter, and answers questions from a script prepared by handlers overseas.
- A clean background check. Because the identity is genuine, the check comes back clean — the employer is verifying a person who exists, not the person typing.
- The laptop. The company ships equipment to an address controlled by the network. From that machine, the worker tries to install remote-access tools, load malware and reach internal systems.
In the KnowBe4 case, the tell came fast: the laptop began beaconing out and loading suspicious software shortly after delivery, and the company's own security team caught it. The firm disclosed the incident publicly and said the fake worker was a North Korean national using a stolen US identity.
The laptop farm: 90 machines on wire shelves in Arizona
A remote job needs a US address, and that is where the laptop farm comes in. Christina Chapman, a woman living in Arizona, kept more than 90 company laptops on wire shelving in her home, each one labeled with the name of the employer that had shipped it and the stolen American identity it was registered to.
Her role was infrastructure. She received the machines, connected them to her home internet so the traffic appeared to come from a US residential address, and kept them running while the workers overseas logged in through remote desktop software. She also helped with the paperwork side — receiving and forwarding payments, and in some cases running the shell companies that collected the salaries.
The money tells the scale. Prosecutors said more than $17 million passed through her house, while Chapman herself kept about $177,000. She was sentenced to 102 months in federal prison in July 2025. She maintained she never knew who she was really working for; prosecutors argued her own messages showed she did.
Why North Korea runs an army of fake remote workers
The program exists because it is cheap, deniable and profitable. Sanctions limit the regime's access to hard currency, and a single well-placed IT worker in a US company can generate a six-figure salary, insider access and extortion leverage at once.
Microsoft Threat Intelligence, which tracks the activity as "Jasper Sleet," describes a structure of operators, identity brokers and facilitators spread across several countries. The FBI's IC3 issued a public service announcement in January 2025 warning US employers that DPRK IT workers routinely use stolen identities, US-based intermediaries and remote tools to hold jobs in American firms. The workers are not freelancers improvising: they are part of an operation whose proceeds fund the state.
The targets are not only tech companies. Any employer that hires fully remote staff and ships equipment to a home address is exposed — staffing agencies, healthcare billing firms, financial services, defense contractors.
The night of the alert: what a compromised laptop looks like
The most instructive part of the case is the timeline inside the company. A newly issued laptop is a controlled environment: IT knows exactly what should be installed on it. Anything else is a signal.
- Unusual outbound connections to infrastructure the company does not use, especially in the first hours after setup.
- Remote-access tools installed without a ticket — legitimate employees ask IT for help; intruders install their own.
- Credential harvesting attempts against internal systems, email and password managers.
- Traffic from a residential IP that does not match the employee's stated location or working hours.
In this case the detection came within minutes of the machine coming online, and the worker's access was cut before deeper damage was done. Most employers do not have that kind of monitoring on a new hire's first day.
The questions employers ask after a case like this
The doubts raised by readers of this story are practical ones. Does a video interview prove anything? No — a live call confirms a face and a voice, not a legal identity, and filters and stand-ins defeat it. Does a background check help? Only if it is matched against biometric and document verification, because the stolen identity is real and will verify cleanly. Does a US address mean a US worker? Not when laptops are collected in a house in Arizona and operated remotely from abroad.
What does work is layered: verifying identity documents with liveness checks, confirming the person on camera matches the documents, requiring in-person or supervised onboarding for sensitive roles, monitoring new devices closely for the first weeks, and treating salary payment routing as a fraud control. Companies that train staff to spot phishing still need to apply the same suspicion to their own hiring pipeline.
What the Chapman case changed
The sentencing of a US-based facilitator to more than eight years is the part of this crime story with the widest consequences. Before the case, laptop farms were treated as an obscure logistical detail; afterward, prosecutors and the FBI began describing them as the choke point of the entire scheme.
Investigators found more houses and more laptops as the case expanded, and the pattern repeated: machines shipped to addresses that looked ordinary, labeled with company names and stolen identities, humming on shelves overnight. The lesson for employers is that the fraud is not only overseas — it has a US footprint of addresses, bank accounts and people willing to host hardware for a fee.
Max Crime reconstructs the case from Department of Justice releases, the FBI's public warning, Microsoft's threat intelligence and reporting by Bloomberg Originals, NBC News, CNN, CBS News, The Wall Street Journal and others, with 3D scenes and video-call screens labeled as reconstructions. The victim companies in the Chapman case are not named because the Justice Department did not name them.
The bottom line
A company that sells fraud detection hired a North Korean operative through a normal job posting, and only its own monitoring caught him. The scheme works because it exploits trust in documents, video calls and US addresses — three things that can all be faked or rented. The Chapman case shows the infrastructure has a domestic layer of homes, shelves and bank accounts, and that facilitators face years in prison for hosting it. For employers, the takeaway is blunt: verify the person, not the paperwork, and watch every new laptop from the moment it powers on.
Key takeaways
- A North Korean IT worker passed four video interviews and a background check at KnowBe4, a company that trains staff to spot fakes, and began loading malware as soon as his work laptop was switched on.
- Christina Chapman of Arizona kept more than 90 laptops on wire shelves in her home, each tagged with a company and a stolen American name, and was sentenced to 102 months in federal prison in July 2025.
- Chapman personally kept about $177,000 while more than $17 million moved through her house.
- The FBI's IC3 warned in a January 2025 public service announcement that DPRK IT workers use stolen identities and remote infrastructure to get hired by US firms.
- Microsoft Threat Intelligence tracks the scheme as 'Jasper Sleet,' a North Korean operation that places IT workers inside Western companies to fund the regime.
Source: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story) · Markdown version
Questions & answers
How did a North Korean IT worker pass a cybersecurity company's hiring process?
He used a real American's stolen identity, an AI-altered photo and scripted answers across four video interviews, so the background check verified a person who genuinely exists. The company shipped a laptop to an address controlled by the network, and malware activity began as soon as the machine came online.
What exactly is a laptop farm?
It is a US location where company-issued laptops are received and kept connected to residential internet, so remote workers abroad appear to be logging in from inside the country. In the Arizona case, more than 90 machines sat on wire shelves, each tagged with an employer and a stolen name.
How much money does the scheme generate?
Prosecutors said more than $17 million moved through Christina Chapman's house, while she personally kept about $177,000 before being sentenced to 102 months in federal prison. Individual salaries for fake IT workers commonly run into six figures per year.
What can a company do to catch a fake hire?
Combine document verification with liveness and biometric checks, confirm the person on camera matches the ID, and monitor new devices closely for the first weeks. Treat payment routing and home addresses as fraud controls, and require supervised onboarding for roles with sensitive access.